Hardening DeepSeek Harness: Architecture, Setup Tutorial, and Runtime Security
AK
Alex Kim Threat intelligence editor · Updated Sep 12, 2026, 10:51 AM EDT
Deploying DeepSeek-R1 agent runtimes? Learn how to harden the harness architecture, configure local inference, mitigate CVEs, and enforce sandbox security.
Software engineering teams evaluating open-source alternatives to proprietary agentic stacks like Anthropic's Claude Code are increasingly turning to community runtimes powered by DeepSeek-R1. Yet migrating to self-hosted coding agents has exposed significant friction: namespace confusion between benchmark suites and execution engines, unpredictable context degradation, and severe host-level security vulnerabilities.
Executing a reliable deployment requires viewing the harness not as a single turnkey binary, but as an architectural pattern. Success hinges on clear separation between benchmarks and dynamic runtimes, deterministic tool execution, and defense-in-depth isolation. This DeepSeek harness setup tutorial walks through the architectural mechanics, local inference configuration, and production-grade sandboxing required to deploy safely.
Dissecting the Harness: Benchmarks Versus Dynamic Runtimes
Much developer friction stems from an unresolved namespace collision between two distinct software paradigms circulating under the label "DeepSeek Harness."
Dimension
Official Benchmark Harness (deepseek-ai/deepseek-harness)
Community Agent Runtime (dsh / HarnessEngine)
Primary Objective
Standardized capability evaluation and static model scoring
Autonomous multi-step software engineering and task execution
Pure compute; zero access to host shell or filesystem
Programmatic invocation of bash, Git, compilers, and test suites
State & Memory
Stateless per benchmark test case
Multi-turn persistence with rolling memory buffers and pinned state
The official evaluation repository published by DeepSeek is a static scoring harness designed to benchmark raw model outputs against predefined academic test sets. It does not inspect local Git repositories or execute terminal commands.
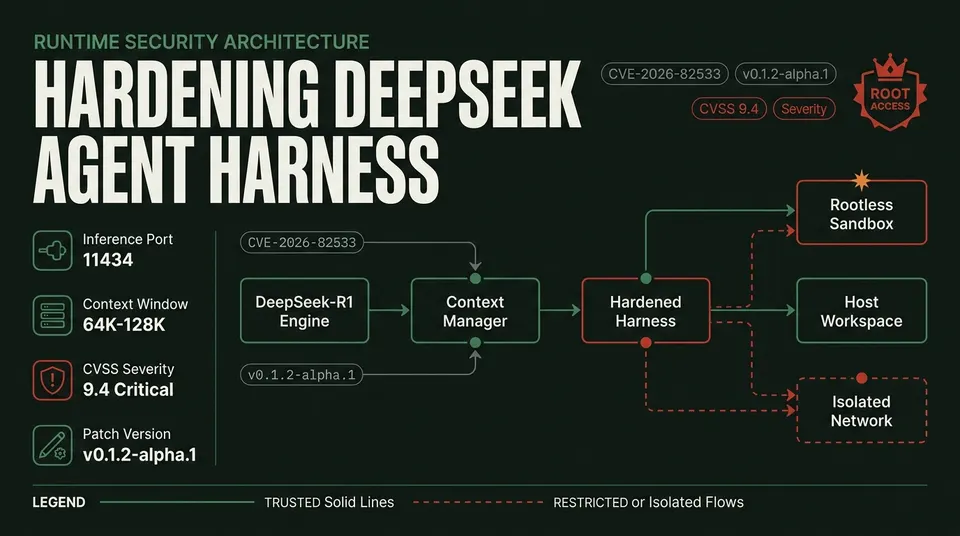
Conversely, community frameworks such as dsh and modular HarnessEngine architectures act as dynamic orchestrators. They bridge DeepSeek-R1 with the host system, establishing an autonomous loop that parses reasoning traces and executes system-level tools.
Observe: Workspace states, file contents, and error outputs are gathered into structured context blocks.
Think: DeepSeek-R1 outputs explicit planning tokens within <think> tags, evaluating previous outputs and planning file refactors before producing machine-readable instructions.
Act: The engine extracts structured tool parameters, validates them against allowed system schemas, and executes the designated routine.
Evaluate: Output streams (STDOUT/STDERR) are captured. If an execution fails, the stack trace feeds directly into the subsequent reasoning step for automated self-correction.
Because multi-step tasks quickly saturate context windows (typically 64K to 128K tokens), production engines enforce rolling eviction for verbose logs beyond 50 lines, apply abstractive summarization when token utilization crosses 70 percent, and pin project directory trees across turns.
Environment Setup and Local Inference Configuration
A reliable harness avoids unconstrained shell wrappers. It enforces explicit path containment, validates schemas, and eliminates arbitrary shell interpolation:
"""
dsh_core.py - Hardened Local Agent Harness for DeepSeek-R1
"""
import os
import subprocess
from typing import Dict, Any, List
from openai import OpenAI

class HardenedHarnessEngine:
 def __init__(self, base_url: str = "http://localhost:11434/v1", api_key: str = "ollama", model: str = "deepseek-r1:14b"):
 self.client = OpenAI(base_url=base_url, api_key=api_key)
 self.model = model
 self.workspace = os.path.abspath("./agent_workspace")
 os.makedirs(self.workspace, exist_ok=True)
 self.messages: List[Dict[str, str]] = [
 {"role": "system", "content": "Sandboxed assistant. Propose actions using valid JSON."}
 ]

 def tool_read_file(self, relative_path: str) -> str:
 """Path-traversal resistant file reader."""
 target_path = os.path.abspath(os.path.join(self.workspace, relative_path))
 if not target_path.startswith(self.workspace):
 return "ERROR: Security violation - path traversal outside workspace forbidden."
 if not os.path.exists(target_path):
 return f"ERROR: File '{relative_path}' not found."
 with open(target_path, "r", encoding="utf-8", errors="replace") as f:
 return f.read()

 def tool_run_sandboxed_command(self, command: List[str]) -> str:
 """Restricted process execution avoiding shell=True."""
 ALLOWED_BINARIES = {"pytest", "git", "ls", "grep", "cat", "python3"}
 if not command or command[0] not in ALLOWED_BINARIES:
 return f"ERROR: Command '{command[0]}' rejected by execution policy."

 try:
 res = subprocess.run(
 command,
 cwd=self.workspace,
 capture_output=True,
 text=True,
 timeout=30,
 shell=False
 )
 return f"STDOUT:\n{res.stdout}\nSTDERR:\n{res.stderr}"
 except subprocess.TimeoutExpired:
 return "ERROR: Process execution timed out after 30 seconds."
 except Exception as e:
 return f"ERROR: Subprocess invocation failed: {str(e)}"
Threat Modeling, Vulnerability Analysis, and Sandboxing
Connecting an autonomous reasoning model directly to host utilities introduces severe attack vectors that must be actively countered.
Vulnerability / Threat
Severity
Mechanism
Impact & Mitigation
CVE-2026-82533
CVSS 9.4 (Critical)
HTTP Host header spoofing in isTrustedApiRequest
Allowed arbitrary callers to bypass authentication, elevate to danger-full-access, and disable the sandbox. Mitigation: Upgrade to DeepSeek Harness v0.1.2-alpha.1 or later; bind local API endpoints strictly to loopback interfaces with TCP peer verification.
Docker Socket Misconfiguration
High
Mounting /var/run/docker.sock inside the container
Allows an agent or compromised dependency to issue direct Docker API calls to escape container boundaries. Mitigation: Never mount the Docker socket into the execution environment.
Isolating the network layer (--network none) prevents data exfiltration. Dropping Linux capabilities (--cap-drop=ALL) and mounting a read-only root filesystem blocks persistence mechanisms and unauthorized binary modification.
Field Assessment: Self-Hosted Stacks Versus Proprietary Ecosystems
Engineering teams evaluating self-hosted DeepSeek harness architectures against proprietary solutions must balance governance advantages against operational maintenance.
Dimension
Community DeepSeek Harness (dsh)
Proprietary Coding Stacks (e.g., Claude Code)
Data Governance
Total Sovereignty: Runs entirely on-premises or air-gapped with zero telemetry egress.
Shared Responsibility: Codebase context and terminal sessions stream to vendor infrastructure.
Token Economics
Cost-Effective: Zero recurring subscription fees on local silicon; low per-token cost via API.
Context Handling
Variable: Requires custom eviction and log truncation to sustain stability beyond 15 turns.
Advanced: Turnkey context management, repository-level caching, and workspace indexing.
High: Demands internal orchestration for GPU workloads, sandbox isolation, and patching.
Minimal: Managed CLI application with immediate enterprise support channels.
Adopting community-driven DeepSeek harness runtimes liberates engineering teams from vendor lock-in and protects sensitive codebases. However, shifting from managed environments places the burden of security and runtime stability entirely on platform engineers. Treating the harness pattern with rigorous discipline—coupling deterministic tool schemas with hardened, patched isolation boundaries—ensures organizations capture the full reasoning power of DeepSeek-R1 without compromising infrastructure integrity.